GDPR

GDPR Compliance Software with Expert Support

Most GDPR compliance tools hand you a policy template and leave the interpretation to you. Carbide’s platform automates data mapping and documentation while advisors answer the questions that don’t have a single right answer.

INTENTIONAL DATA PROTECTION LEADS TO FASTER COMPLIANCE

DRIVE security & privacy by design
Achieve compliance by default

Everything you need for GDPR compliance

  • GDPR Plan

    GDPR Plan

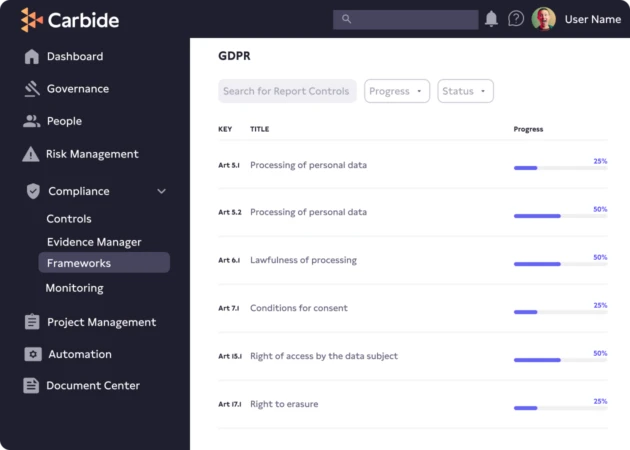
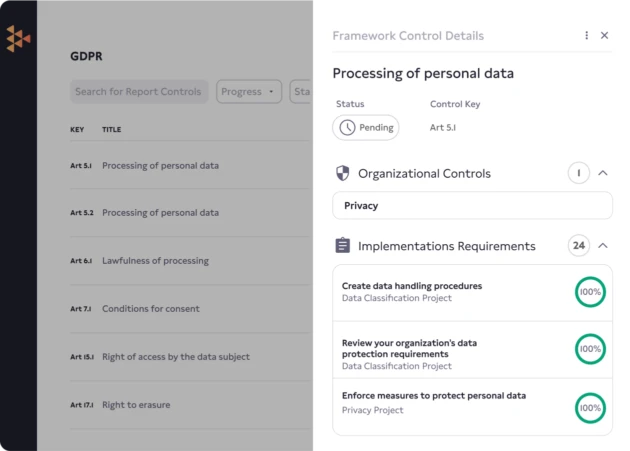
    Step by step implementation plan outlines every GDPR regulation and requirement

  • Customized Policies

    Customized Policies

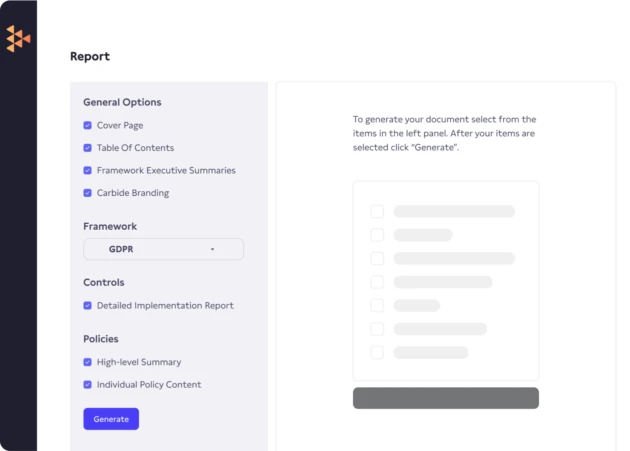
    Our automated policy builder ensures your policies meet GDPR requirements

  • Policy Management

    Policy Management

    Reduce admin time with automated employee reminders and tracking

  • Security Awareness Training

    Security Awareness Training

    In-platform Carbide Academy videos on security and privacy best practices with a template library for common requirements

  • Evidence Collection

    Evidence Collection

    100+ technical integrations connecting to your tech stack to automatically capture your compliance with GDPR

  • Audit Support

    Audit Support

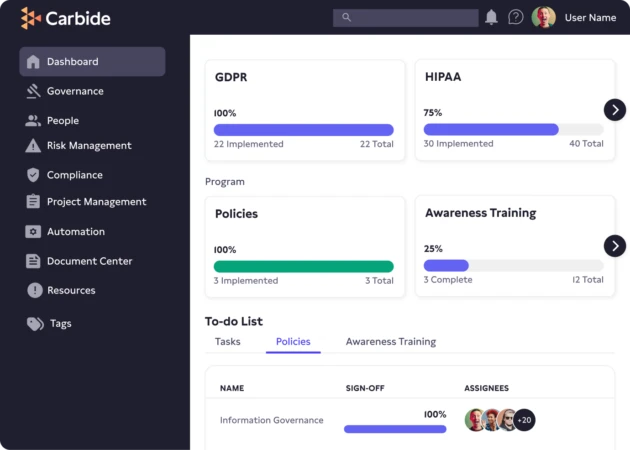
    Save time by giving auditors a read-only view of your GDPR reporting dashboard

  • Robust Ecosystem

    Robust Ecosystem

    Carbide’s security and privacy services and network of audit partners help you meet requirements faster


  • Multi-Compliance by Design

    Multi-Compliance by Design

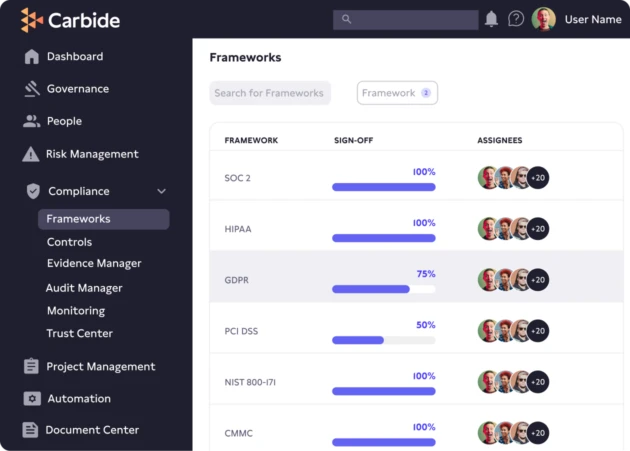
    Comply with multiple frameworks & regulations with our unified platform

  • Cloud Monitoring

    Cloud Monitoring

    Easily collect data with automated security monitoring, security assessments, and remediation tools to make actionable insights on your cloud environment

Frequently Asked Questions

What is GDPR?

GDPR stands for the General Data Protection Regulation. It protects the personal data of people in the European Union and went into effect in May of 2018. The GDPR ensures that companies are held accountable for keeping personal information safe. Although this law was created in the European Union to protect the data of its citizens, it affects companies that deal with worldwide business and handle data around the world. The GDPR set new standards for global privacy and initiated a wave of similar laws globally.

What is data protection by design and default?

This principle within the GDPR institutes Privacy by Design as a primary element of data protection in which technologies are designed to include privacy as a default function rather than an option. In this way, when a user accesses a website or service, privacy safeguards are built in from the start.

What is the data processor?

Under the GDPR, the data processor is a third party that processes personal data on behalf of the data controller. The processor does not own the data and acts on the controller’s instructions.

How long does GDPR implementation take?

There is no single timeline; it depends on the size of your organization, how much personal data you process, and how much of your data mapping and documentation already exists. What slows most organizations down is starting from a blank page. Carbide shortens the process by generating your records of processing activities, tailored policies, and pre-populated tasks from a structured gap analysis, so your team can spend its time on remediation.

How do I stay audit-ready?

GDPR audits may be scheduled internally, triggered by customer requests, or initiated by regulators. Audit readiness comes down to evidence, which includes training completion records, policy sign-offs, and technical control data. Carbide’s 100+ integrations collect that evidence continuously, and auditors can be given read-only access to your GDPR reporting dashboard instead of a manual document handover.

Does the GDPR apply to my business?

The GDPR regulates what companies can do with the personal data of people located in the EU, based on factors such as offering them goods or services or monitoring their behavior. These regulations apply to any business (including those based in the U.S. and Canada) that meets those conditions. The most important feature of this privacy law is that it gives individuals more rights and control over what your business does with their data and whether they wish to consent to the collection of their data by your business.

What is Pseudonymization?

Under the GDPR, pseudonymization is a safeguard that can help protect personal data. Pseudonymization is the process that transforms how data is stored in a way that will make the final data not attributable to a specific data subject (an individual) without using any additional information. Pseudonymization is a lighter-touch alternative to complete data anonymization. An example of pseudonymization is encryption used as a pseudonymization transformation, where the decryption key is stored and managed separately from the data.

What is the data controller?

As the title suggests, the data controller is in charge of data, and they have the most responsibility with regard to the protection of privacy and the rights of data subjects. The controller may also be the collector of data.

Under GDPR, the controller must provide required information about their data collection practices, disclose the lawful basis for and the purpose for data processing, and state the timeframe for data processing and retention. Controllers must also disclose if the data collected is being shared with any third parties or transferred outside of the EEA.

What documentation does GDPR require?

Core documentation includes records of processing activities, data protection policies, lawful bases for each processing activity, data processing agreements with vendors, and evidence of measures such as training and access controls. Carbide auto-generates this documentation and keeps it current as your products, vendors, and markets change, so it reflects how you actually operate now rather than how you operated at your last annual review.

Does GDPR compliance end after implementation?

No. GDPR is an ongoing obligation. Your obligations shift as you add products, enter new markets, onboard vendors, and as regulatory guidance evolves. Carbide’s automated compliance checks continuously evaluate your data protection framework, flag new gaps, and update your documentation, so your compliance posture keeps pace with your business.

See How Carbide Can Help You

Schedule a consultation with one of our Data Protection Solutions Advisors to learn how Carbide can accelerate your security & privacy program.

This field is for validation purposes and should be left unchanged.
By submitting this request you consent to receive emails from Carbide. You can opt-out from receiving emails at any time.