ISO 27001

ISO 27001 Compliance Software with Expert Support

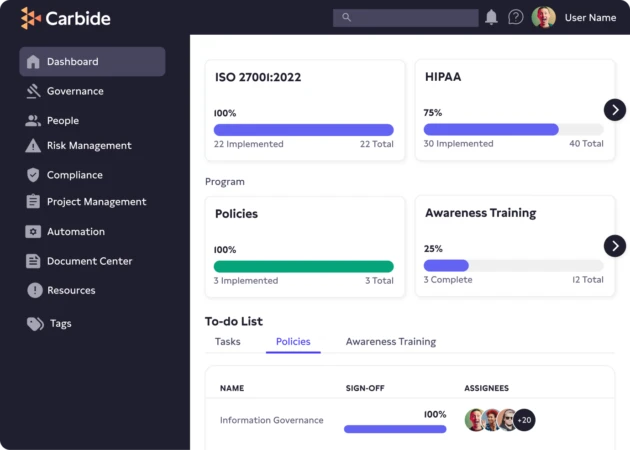
Your information security management system has to work in practice, not just on paper. Carbide’s platform tracks your controls continuously so you reach audit readiness faster, and our advisors help you close the gaps that an external auditor will look for first.

STRONGER SECURITY LEADS TO FASTER COMPLIANCE

DRIVE security & privacy by design
Achieve compliance by default

Everything you need for ISO 27001 compliance

  • ISO 27001 Plan

    ISO 27001 Plan

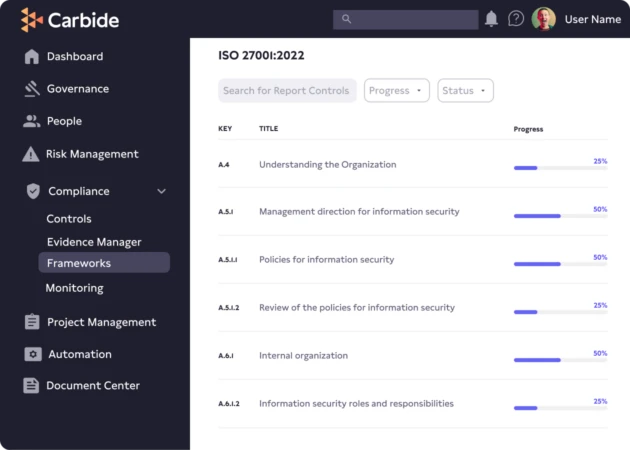
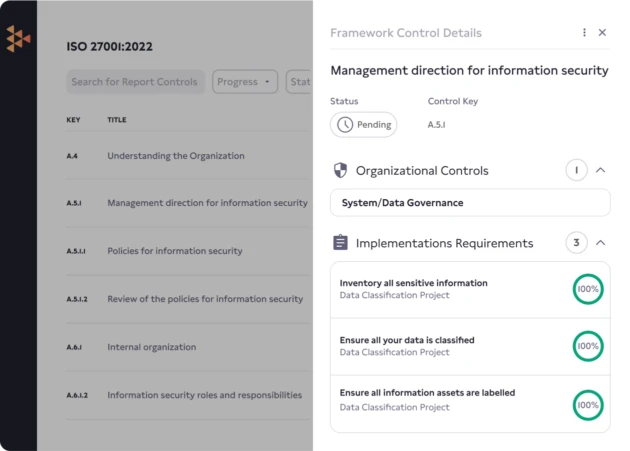
    Step by step implementation plan outlines every ISO 27001 control and requirement

  • Customized Policies

    Customized Policies

    Our automated policy builder helps ensure your policies meet ISO 27001 requirements

  • Policy Management

    Policy Management

    Reduce admin time with automated employee reminders and tracking

  • Security Awareness Training

    Security Awareness Training

    In-platform Carbide Academy videos on security and privacy best practices with a template library for common requirements

  • Evidence Collection

    Evidence Collection

    100+ technical integrations connecting to your tech stack to automatically capture your compliance with ISO 27001

  • Audit Support

    Audit Support

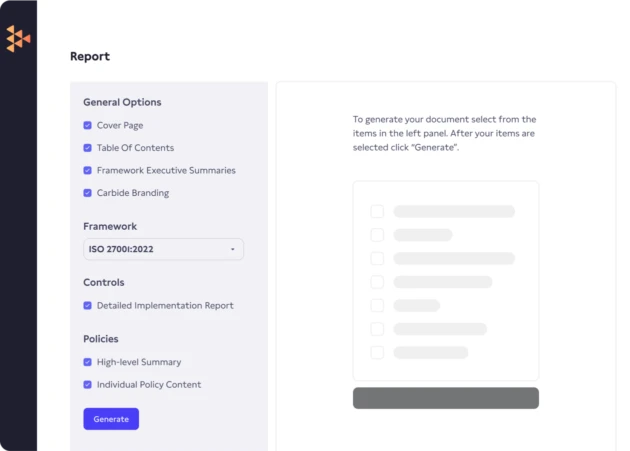
    Save time by giving auditors a read-only view of your ISO 27001 reporting dashboard

  • Robust Ecosystem

    Robust Ecosystem

    Carbide’s security and privacy services and network of audit partners help you meet requirements faster


  • Multi-Compliance by Design

    Multi-Compliance by Design

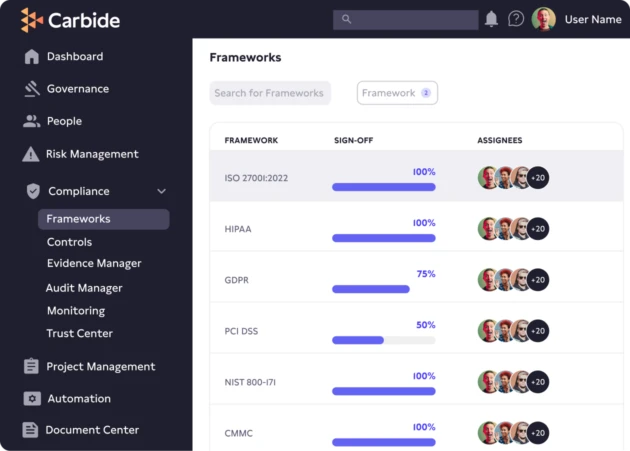
    Comply with multiple frameworks & regulations with our unified platform

  • Cloud Monitoring

    Cloud Monitoring

    Easily collect data with automated security monitoring, security assessments, and remediation tools that turn findings into actionable next steps for your cloud environment

Frequently Asked Questions

What is ISO 27001?

ISO 27001 is an international standard for managing information security and data protection. It specifies the requirements for an Information Security Management System (ISMS), a framework for identifying the information an organization needs to protect and selecting the controls to do so. Officially known as ISO/IEC 27001, it was developed by the International Organization for Standardization and the International Electrotechnical Commission. The current version is ISO/IEC 27001:2022.

What is the difference between ISO 27001 and ISO 27002?

ISO 27001 is a security framework that lays out a set of requirements that must be met for businesses to achieve certification. Meanwhile, ISO 27002 is a supporting document that provides additional details and advice for meeting those certification requirements. There are no audits or certifications for ISO 27002, as it is a guidance document only.

How much does ISO 27001 cost?

The cost of ISO 27001 implementation and certification varies based on factors such as your ISMS scope, organization size and complexity, existing security posture, and any external resources required. Certification costs also vary by certification body. Using an information security management platform like Carbide can dramatically reduce the time and resources needed to achieve and maintain certification.

How long does it take to get ISO 27001 certified?

Organizations often reach certification in 6 to 12 months, depending on company size, ISMS scope, and how mature the existing security program is. A structured implementation plan and automated evidence collection compress that timeline by removing the manual work of building policies, mapping controls, and gathering audit evidence from scratch. Assess your ISO 27001 readiness to see where you stand.


What happens when my ISO 27001 certificate expires?

ISO 27001 certificates are valid for three years. Before expiration, your certification body will perform a recertification audit: a fuller review than a surveillance audit that examines the entire ISMS again. A program maintained through continual improvement helps keep this manageable.


Who uses the ISO 27001 framework?

ISO 27001 is a globally recognized security framework for building and maintaining an Information Security Management System meant to protect information and prevent privacy risks in your organization. Organizations use ISO 27001 to ensure and demonstrate data security, as well as mitigate risks and prevent data breaches. It can also be used to meet compliance requirements of data protection regulations.

How many controls are in ISO 27001?

Annex A of ISO/IEC 27001:2022 lists 93 controls grouped into four themes: organizational, people, physical, and technological. You don’t necessarily need all 93; your risk assessment determines which controls apply, and you document those decisions in a Statement of Applicability. These controls are all in the Carbide platform, complete with compliant policies that are automatically customized for your organization and an Implementation Plan that guides you through required action items.

Does my business need an audit to be ISO 27001 certified?

An organization can assess its own conformity with ISO 27001, but this is different from third-party certification. To become ISO 27001 certified, an organization must complete a certification audit conducted by an independent certification body. The certification process includes two stages: Stage 1 reviews the ISMS documentation and readiness, while Stage 2 assesses whether the ISMS has been implemented and is operating effectively.

What is a surveillance audit?

Certification is not a one-time event. Your certification body will conduct surveillance audits, typically once a year in the two years following certification, to confirm your ISMS is still operating as documented. Organizations that let their program go quiet between audits often scramble at surveillance time, while teams tracking controls year-round treat it as a routine check-in. Our advisors help teams stay ready between audits, not simply for the first one.

What does continual improvement mean in ISO 27001?

ISO 27001 requires your ISMS to improve over time. In practice, that means running internal audits, holding management reviews, tracking corrective actions to resolution, and updating your risk assessment as your environment changes. Many organizations use the plan-do-check-act cycle to structure this work, although the standard doesn’t require a particular method. Doing it consistently is what keeps your certification defensible at every surveillance and recertification audit.

See How Carbide Can Help You

Schedule a consultation with one of our Security Solutions Advisors to learn how Carbide can accelerate your path to ISO 27001 certification and keep your program strong afterward.

This field is for validation purposes and should be left unchanged.
By submitting this request you consent to receive emails from Carbide. You can opt-out from receiving emails at any time.