HIPAA

HIPAA Compliance Software with Expert Support

Getting HIPAA-compliant is achievable. Staying compliant as you add vendors, expand your product, and sign new business associate agreements is where most teams fall short. Carbide handles both.

INTENTIONAL DATA PROTECTION LEADS TO FASTER COMPLIANCE

DRIVE security & privacy by design
Achieve compliance by default

Everything you need for HIPAA compliance

  • HIPAA Plan

    HIPAA Plan

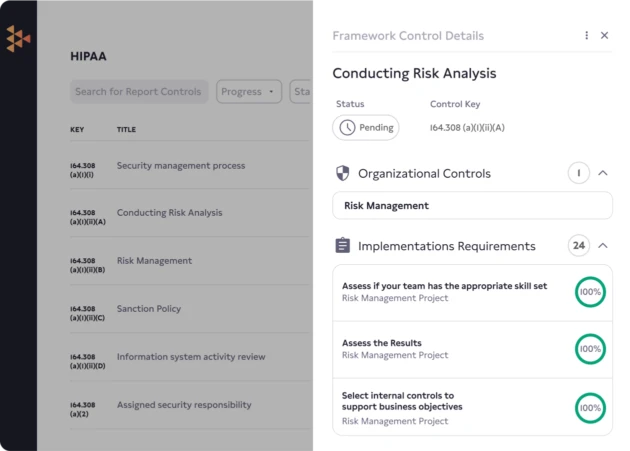
    Step-by-step implementation plan outlines every HIPAA control and requirement

  • Customized Policies

    Customized Policies

    Our automated policy builder ensures your policies meet HIPAA requirements

  • Policy Management

    Policy Management

    Reduce admin time with automated employee reminders and tracking

  • Security Awareness Training

    Security Awareness Training

    In-platform Carbide Academy videos on security and privacy best practices with a template library for common requirements

  • Evidence Collection

    Evidence Collection

    100+ technical integrations connecting to your tech stack to automatically capture your compliance with HIPAA

  • Audit Support

    Audit Support

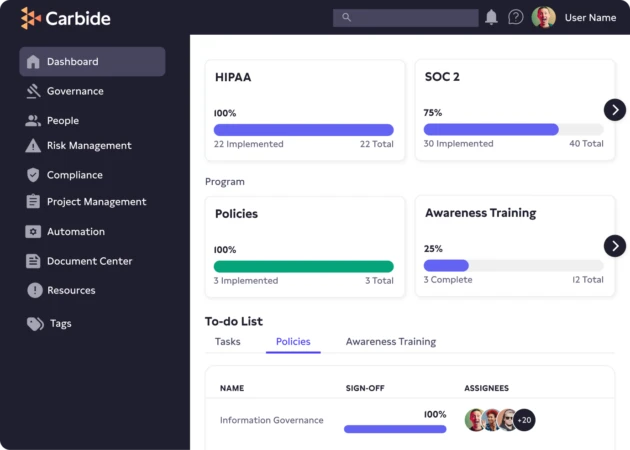
    Save time by giving auditors a read-only view of your HIPAA reporting dashboard

  • Robust Ecosystem

    Robust Ecosystem

    Carbide’s security and privacy services and network of audit partners help you meet requirements faster


  • Multi-Compliance by Design

    Multi-Compliance by Design

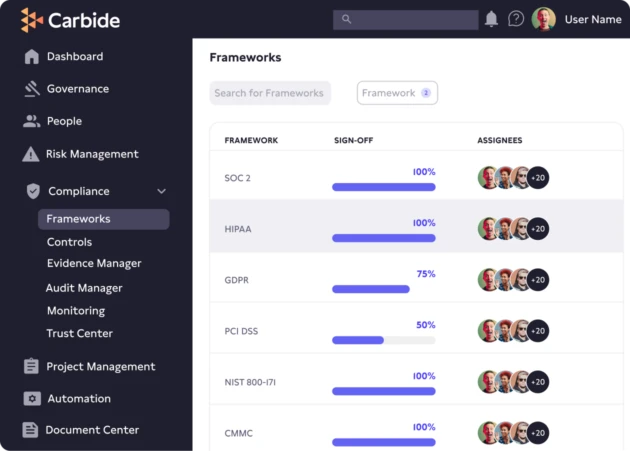
    Comply with multiple frameworks & regulations with our unified platform

  • Cloud Monitoring

    Cloud Monitoring

    Easily collect data with automated security monitoring, security assessments, and remediation tools that turn insights about your cloud environment into actionable steps

Frequently Asked Questions

What businesses must be HIPAA compliant?

Healthcare providers, health plans, and healthcare clearinghouses in the U.S. that qualify as covered entities, along with their business associates, must comply with the applicable HIPAA requirements, including those under the Security, Privacy, and Breach Notification Rules. Business associates are third-party service providers that handle protected health information (PHI) on behalf of covered entities.


What is protected health information?

Protected health information, or PHI, is individually identifiable health information created, received, maintained, or transmitted by covered entities and their business associates. As an example, this could include data stored and transmitted by a technology service that provides email or text-based appointment reminders.

What safeguards are required to protect PHI?

The proper technical, physical, and administrative safeguards must be in place to protect the confidentiality, integrity, and availability of all PHI. This means protecting PHI against reasonably anticipated threats to its security or integrity and impermissible uses or disclosures. The Carbide platform guides you through establishing a foundation of HIPAA-compliant security policies and the action items required to ensure your PHI is safeguarded.

What is a HIPAA risk analysis?

A HIPAA risk analysis is an assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic protected health information (ePHI). It helps an organization identify threats, evaluate existing safeguards, and determine what measures are needed to reduce risks and meet HIPAA Security Rule requirements.

How can my business prepare for HIPAA compliance?

Start by identifying the PHI your organization handles, where it resides, and which vendors can access it. Conduct the required risk analysis, document applicable policies and procedures, and address identified gaps with appropriate safeguards. Maintain supporting evidence and review your program as your systems and business relationships change.

Can my business work toward HIPAA and SOC 2 compliance at the same time?

Yes. Organizations pursuing both may be able to reuse relevant policies, controls, and evidence where requirements overlap. However, HIPAA and SOC 2 have different purposes and requirements, so meeting one does not automatically satisfy the other. Carbide helps organizations manage multiple frameworks through our unified platform.

What is a Business Associate Agreement?

A Business Associate Agreement (BAA) is a contract required between a covered entity like a hospital or other healthcare provider and a business associate that handles PHI on its behalf. The BAA outlines each party’s responsibilities for protecting PHI and sets out the business associate’s obligations under HIPAA. This means that if you are transmitting PHI to another service provider, having that service provider sign a BAA establishes their responsibilities for protecting that information.

Learn more in our guide, “What is a HIPAA Business Associate Agreement?”

Does my business need to get an audit to be HIPAA certified?

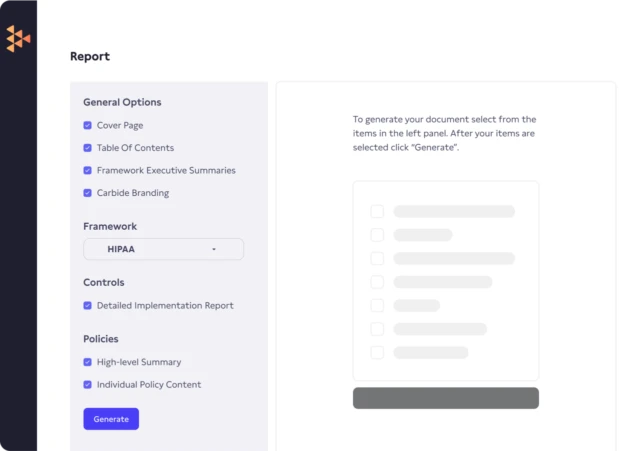
There is no officially endorsed HIPAA certification, and therefore, no audits are required to be certified. Though companies are permitted to sell “certification” audits and services, these are not required by HIPAA for compliance. Under HIPAA, organizations must perform a periodic review of all technical and non-technical requirements, including security policies and procedures. This can be done internally using an information security management platform like Carbide to identify gaps in compliance and generate reports.

What happens if a business associate is not compliant with HIPAA?

Under the law, business associates can be held directly liable for HIPAA violations. Failure to comply with the regulatory requirements, such as the Security Rule or providing breach notifications, can result in enforcement action by the HHS Office for Civil Rights.

How long does it take to become HIPAA compliant?

The time required to work toward HIPAA compliance depends on your organization’s size, the systems and vendors involved, your existing security practices, and the gaps that need to be addressed. Organizations with established controls may need less implementation work than those building a program from the ground up.

Carbide’s implementation plan helps your team identify requirements, prioritize tasks, and track progress, while expert guidance helps you understand what needs attention. The timeline ultimately depends on your organization’s specific needs and how quickly identified gaps can be addressed.

Does HIPAA compliance software make my business compliant?

Software can help your organization manage policies, assign tasks, track controls, and collect evidence, but using a platform alone does not guarantee HIPAA compliance. Your team still needs to understand its obligations, assess risks, implement appropriate safeguards, and maintain its compliance program. Carbide combines compliance management software with expert guidance to help map requirements to your organization’s data flows and vendor relationships, identify gaps, and manage the work needed to address them.

Take the Next Step Toward HIPAA Compliance

Schedule a consultation with one of our HIPAA compliance advisors to discuss your needs and learn how Carbide can strengthen your security and privacy program.

This field is for validation purposes and should be left unchanged.
By submitting this request you consent to receive emails from Carbide. You can opt-out from receiving emails at any time.