SOC 2

SOC 2 Compliance Software with Expert Support

Getting to SOC 2 fast matters. Staying audit-ready as your product and infrastructure evolve matters more. Carbide automates the evidence and puts advisors behind the controls so both happen at once.

STRONGER SECURITY LEADS TO FASTER COMPLIANCE

DRIVE security & privacy by design
Achieve compliance by default

Everything you need for SOC 2 compliance

  • SOC 2 Plan

    SOC 2 Plan

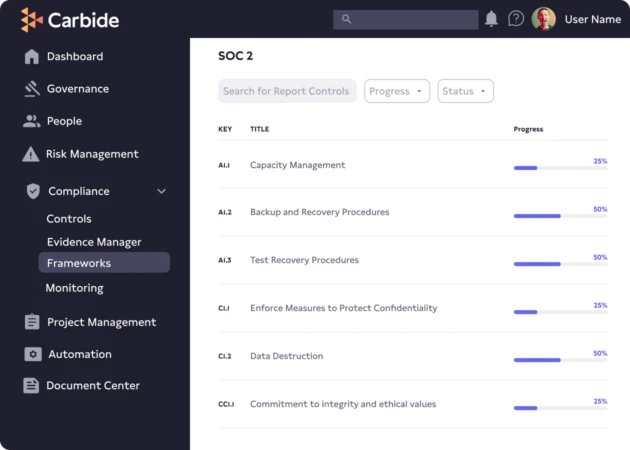
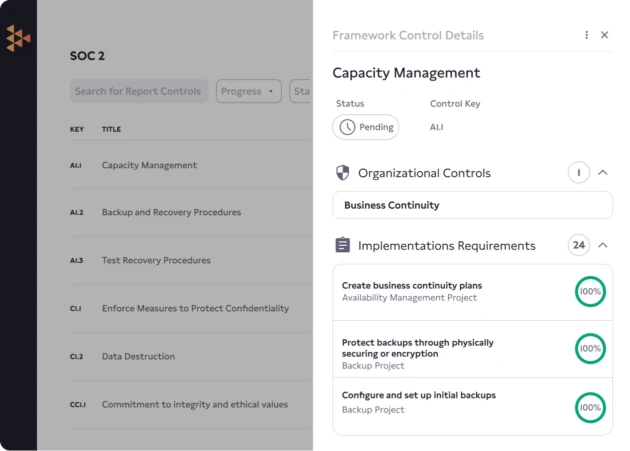
    Step-by-step implementation plan outlines every SOC 2 control and requirement

  • Customized Policies

    Customized Policies

    Our automated policy builder ensures your policies meet SOC 2 requirements

  • Policy Management

    Policy Management

    Reduce admin time with automated employee reminders and tracking

  • Security Awareness Training

    Security Awareness Training

    In-platform Carbide Academy videos on security and privacy best practices with a template library for common requirements

  • Evidence Collection

    Evidence Collection

    100+ technical integrations connecting to your tech stack to automatically capture your compliance with SOC 2

  • Audit Support

    Audit Support

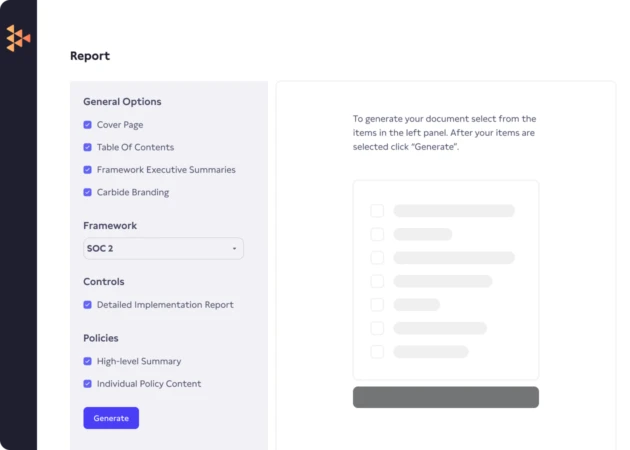
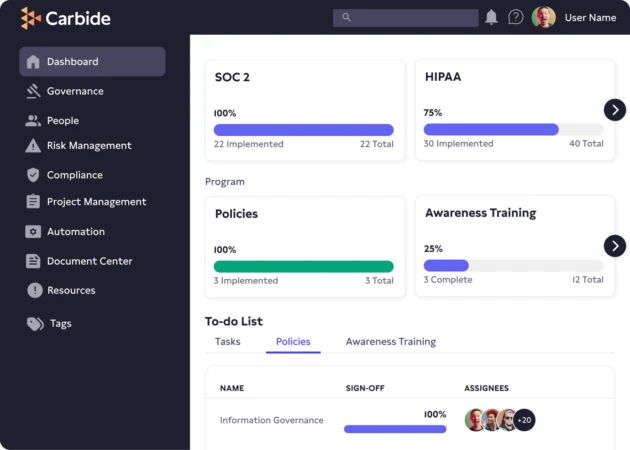
    Save time by giving auditors a read-only view of your SOC 2 reporting dashboard

  • Robust Ecosystem

    Robust Ecosystem

    Carbide’s security and privacy services and network of audit partners help you meet requirements faster


  • Multi-Compliance by Design

    Multi-Compliance by Design

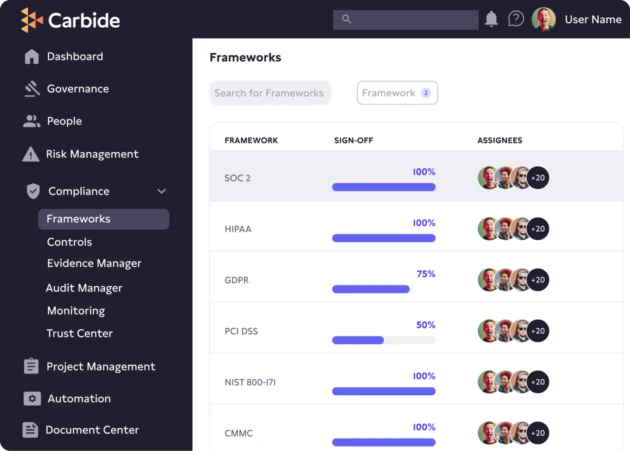
    Comply with multiple frameworks & regulations with our unified platform

  • Cloud Monitoring

    Cloud Monitoring

    Easily collect data with automated security monitoring, security assessments, and remediation tools to make actionable insights on your cloud environment

Frequently Asked Questions

What is a SOC 2 report?

Service Organization Control 2 reports were designed by the AICPA to audit the existence and effectiveness of security, availability, processing integrity, confidentiality, and privacy controls at organizations. These reports are commonly used to assess and provide information and verify a third-party vendor’s data management processes.

What are the SOC 2 requirements?

SOC 2 requirements are based on the 2017 Trust Services Criteria for Security, Availability, Processing Integrity, Confidentiality, and Privacy. These control criteria are included in the Carbide platform, integrated, and mapped to your customer policies, procedures, and implementation plan.

What is SOC 2 Type II certification?

First, there is no such thing as a SOC 2 certification. Proving SOC 2 Type II compliance is the result of an auditor’s report that verifies your company can securely manage and protect data during its operations and for its clients. This third-party attestation, including the auditor’s opinion about the effectiveness of the controls, provides assurance that a service provider is able to meet the Trust Services Criteria for data security.

How long does SOC 2 compliance take?

Timelines depend on your existing security posture and which report you’re pursuing. A Type I report can often be completed in weeks once controls are documented, since it evaluates a single point in time. A Type II report requires an observation window of several months to a year to prove controls performed consistently. Carbide’s advisors help you build a realistic timeline based on your environment and customer deadlines.

What should I expect during a SOC 2 audit?

Auditors will request evidence tied to each control in scope, ask your team to walk through how specific processes work in practice, and follow up on any gaps between your documented policies and what your systems show. Expect this to happen over several weeks of back-and-forth rather than a single sit-down.

Who can perform a SOC 2 audit?

A SOC 2 audit must be conducted by an independent, certified CPA firm. Carbide provides a customized information security program with policies, an implementation plan/checklist, and expert guidance to ensure your company is successfully prepared for your SOC 2 audit.

What is the difference between SOC 1 vs SOC 2 reports?

SOC 1 (Types I and II) reports are focused on the processing of financial information. SOC 2 reports are specific to the security controls related to processing data. A SOC 2 Type I is a point-in-time report that evaluates and tests the design of your information security controls. A SOC 2 Type II report is completed over an extended period of time to test the implementation and effectiveness of your information security program.

Who does SOC 2 apply to?

SOC 2 reports may be used by service organizations to provide security assurance to clients during the sales process, meet compliance with regulatory requirements, or manage governance and risk management. SOC 2 has become a standard for B2B vendors and SaaS companies.

What documentation do I need for a SOC 2 audit?

Auditors expect written policies covering access control, incident response, change management, and vendor risk, plus evidence the policies are actually followed, such as access logs and training records. Carbide generates AI-drafted, SOC 2-aligned policies, and platform integrations pull supporting evidence directly from your tech stack.

What are common SOC 2 compliance challenges?

Teams pursuing SOC 2 without dedicated support often run into the same obstacles: policies that sound compliant but don’t reflect actual practice, audit scope that’s too broad or too narrow, and evidence gaps that appear as infrastructure changes mid-cycle. Carbide’s advisors keep policies grounded in reality, while continuous monitoring catches evidence gaps before the auditors do.

See How Carbide Can Help You

Book a demo with one of our Security Solutions Advisors to learn how Carbide can fast-track your SOC 2 compliance and keep you audit-ready year-round.

This field is for validation purposes and should be left unchanged.
By submitting this request you consent to receive emails from Carbide. You can opt-out from receiving emails at any time.