


Update, July 13, 2026: The Department of War has suspended CMMC Phase II, the mandate that would have required third-party (C3PAO) Level 2 certification starting November 10, 2026. A 60-day Reform Task Force is now reviewing the program’s future. Self-assessment requirements, SPRS scoring, annual affirmations, and DFARS 252.204-7012 remain fully in force and are still enforced under the False Claims Act.
If your prime contractor requires a Level 2 certificate on its own terms, that requirement has not changed. For everyone else, an accurate, advisor-reviewed self-assessment is now the main compliance requirement. Read what actually changed and what to do next, or talk to a Carbide advisor.
With the latest updates to CMMC 2.0 in October 2024, compliance has become an essential step for any organization aiming to engage with the U.S. Department of Defense (DoD). But these requirements aren’t limited to American companies—Canadian organizations in the DoD supply chain or those looking to secure DoD contracts must also meet these cybersecurity standards.
From government agencies to private defense contractors and aerospace companies, Canadian entities face unique challenges when navigating U.S. compliance frameworks. However, as we’ll explore, meeting the CMMC 2.0 requirements can be achieved with structured support. In fact, Carbide recently helped Protocase, a Canadian manufacturing leader, streamline its CMMC 2.0 compliance journey.
Why Canadian Organizations Should Care About CMMC 2.0
The CMMC 2.0 framework establishes a three-tiered certification system that reflects the sensitivity of information managed by contractors, from basic cyber hygiene at Level 1 to advanced security practices at Level 3. For Canadian companies working within the DoD supply chain, achieving CMMC certification is essential—not only for compliance but also to maintain trust with U.S. partners and secure competitive advantages.
Learn more from an CMMC Registered Practitioner
Are you curious about how your organization can streamline CMMC 2.0 compliance?
Watch our CMMC 2.0 on-demand webinar, featuring Darren Gallop, a CMMC Registered Practitioner and CEO of Carbide. Darren shares insights into the compliance journey and offers practical advice on navigating CMMC requirements efficiently.
Canadian Organizations Impacted by CMMC 2.0
- Government Bodies: Canadian government agencies collaborating with the DoD or U.S. defense partners need to ensure compliance.
- Private Sector Companies: Aerospace, technology, manufacturing, telecommunications, and defense companies providing products or services to the DoD must meet CMMC 2.0 standards.
The Canadian Equivalent to CMMC 2.0: Canadian Program for Cyber Security Certification
In addition to the U.S. Department of Defense’s CMMC 2.0, Canadian organizations should be aware of the upcoming Canadian Program for Cyber Security Certification (CPCSC). The CPCSC is Canada’s initiative to enhance the cybersecurity resilience of its defense supply chain, closely aligning with the U.S. CMMC 2.0 framework.
Key Similarities Between CMMC 2.0 and CPCSC:
Both programs feature three certification levels to address varying degrees of cybersecurity requirements and align with NIST SP 800-171 and 800-172, ensuring smooth compliance for organizations operating in both Canadian and U.S. defense sectors.
Case Study: How Protocase Prepared for CMMC Using Carbide’s Support
Protocase, a Canadian manufacturer in aerospace and defense, leveraged Carbide’s expertise to streamline its path to CMMC 2.0 compliance by first achieving NIST 800-171 and DFARS standards.
“By aligning our practices with NIST 800-171 standards early on, we were able to lay the groundwork for CMMC compliance and position ourselves as a reliable partner in the DoD supply chain,” said Steve Lilley, Protocase’s President. Watch the case study to learn how Carbide helped Protocase fast-track its CMMC 2.0 compliance journey.
Implementation Timeline for CPCSC
CPCSC Level 1 became available to suppliers on April 1, 2026. Level 1 requirements begin appearing in select defence contracts from summer 2026, and at that point holding Level 1 certification becomes a condition of eligibility for the contracts that carry the requirement. The program is being phased into specific solicitations rather than applied across the entire defence supply chain at once.
Is your program ready for CPCSC Level 1?
CPCSC Level 1 is being introduced into select DND contracts, and becomes a requirement for the contracts that carry it. If you are not certain your current controls meet the standard, Carbide’s CPCSC Level 1 Readiness Assessment gives you a clear picture of where you stand before your contract window opens.
Mapping NIST 800-171 Controls to CMMC 2.0 Levels
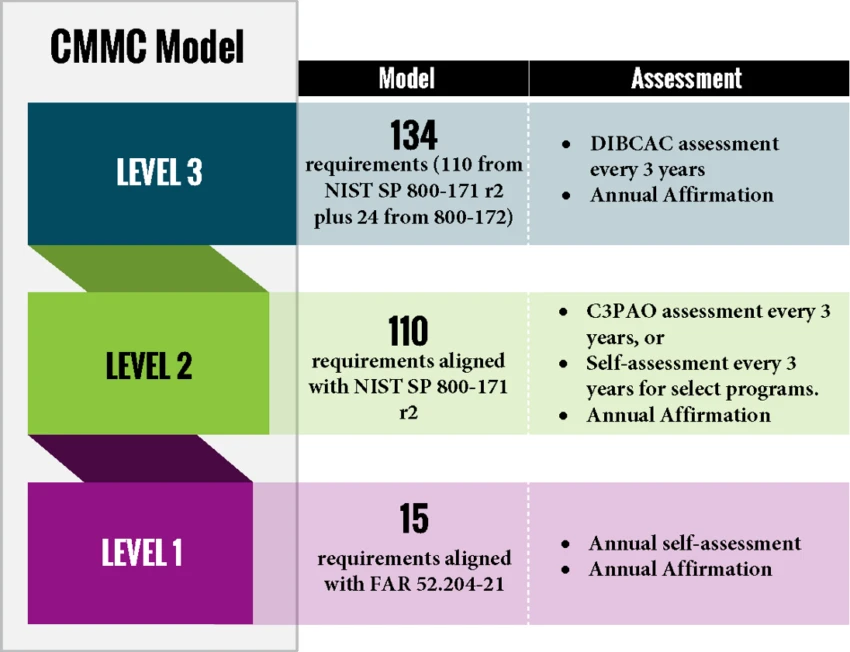
Updated CMMC Model (Source)
For Canadian companies like Protocase, implementing the NIST 800-171 framework provides a substantial head start in meeting CMMC 2.0 requirements. NIST 800-171’s controls overlap significantly with those in CMMC 2.0, especially at Levels 2 and 3.
CMMC Level 1: Foundational
For organizations only needing Level 1, compliance with fundamental cybersecurity practices, such as basic data protection and physical security, is required. Organizations must meet the 15 security requirements outlined in FAR clause 52.204-21.
CMMC Level 2: Advanced
At this level, controls from NIST 800-171 are highly applicable. Organizations must implement 110 security requirements from NIST SP 800-171 Revision 2 to safeguard controlled unclassified information (CUI) – making it a significant head start for companies already compliant with NIST 800-171.
As of the July 2026 Phase II suspension, the requirement that would have mandated third-party (C3PAO) certification for Level 2 is paused pending a program review. The 110 NIST SP 800-171 requirements, SPRS scoring, and annual affirmations remain fully in force, and contracts can currently carry Level 1 (Self) or Level 2 (Self) designations. Prime contractors are not bound by the federal pause and may still require Level 2 certification on their own terms.
CMMC Level 3: Expert
Level 3 is designed for high-value defense contractors working with critical DoD systems and requires more advanced, specialized controls in addition to NIST 800-171. The same 110 security requirements from NIST SP 800-171 Revision 2 is required plus additional 24 requirements derived from NIST SP 800-172.
Steps for Canadian Organizations to Achieve CMMC 2.0 Compliance
Canadian companies that proactively pursue CMMC compliance are not only better positioned to secure DoD contracts but also demonstrate their commitment to cybersecurity and trustworthiness. Compliance with CMMC also builds a reputation that can open doors to new market opportunities within the U.S. defense sector.
Here’s a checklist Canadian organizations can follow to prepare for CMMC 2.0:
- Conduct a gap analysis to see where you stand with CMMC 2.0 requirements.
- Implement and build on existing controls you have in place based on your results from a gap analysis.
- Perform a self-assessment. This satisfies CMMC Level 1, and establishes your Level 2 (Self) status for contracts that permit self-assessment under 32 CFR 170.16. Level 2 contracts that require a third-party (C3PAO) certification under 32 CFR 170.17 are not satisfied by self-assessment alone. Which path applies is determined by the contract.
CMMC 2.0 Level 1 | Free Self-Assessment
If you’re preparing for CMMC 2.0 Level 1 compliance, Carbide’s CMMC 2.0 Level 1 Self-Assessment Tool will give you a report that includes an overall readiness score for CMMC Level 1 self-attestation, a breakdown across all 6 control families, and a prioritized gap list with NIST SP 800-171 control references and recommended actions.
Let Carbide Guide You on Your CMMC 2.0 Journey
For Canadian organizations in the DoD supply chain, CMMC compliance remains a core requirement for doing business, even as the program’s assessment structure is under review. Carbide is here to help you navigate this journey, with Canadian-specific expertise and proven success in guiding companies like Protocase to CMMC 2.0 compliance.
Ready to streamline your CMMC 2.0 compliance journey? Schedule a demo with Carbide today to learn how we can help you fast-track your path to CMMC 2.0 compliance.
Share
